
The SOAR Era Is Over: Why Playbook Automation Can't Catch an Autonomous Attacker
Attackers break out in 29 minutes, sometimes in seconds. SOAR playbooks were built for threats that repeat. Here's why that gap is now a CISO problem.
Read Now
The SOAR Era Is Over: Why Playbook Automation Can't Catch an Autonomous Attacker
Attackers break out in 29 minutes, sometimes in seconds. SOAR playbooks were built for threats that repeat. Here's why that gap is now a CISO problem.
AI-Induced Incidents: The IR Category CISOs Aren't Prepared For
AI-induced incidents don't fit your IR plan, your insurance policy, or your board deck. Here's why CISOs need a new category, now.
Wasted Digital Ink
Why a signed letter calling for global cyber defense commits to nothing, and what a real commitment from the signatories would look like.
WindowsAudit, Part Three: How an IR Investigation Ended in a Police Arrest
The WindowsAudit case ended in an Israeli police arrest. How a routine file check became a nationwide investigation, and how IR work holds up as evidence.
Stolen Thoughts: How Encrypted AI Reasoning Leaked API Keys and Passwords
Researchers decoded 315,320 encrypted reasoning blocks from public AI agent logs and extracted 704 secrets by replaying blocks into weaker, jailbroken models.
Google Hid Its Quantum Result Behind a Proof. It Did Not Stay Hidden.
What Trail of Bits actually did with Google's ZKP, and how the community reconstructed the circuit from prior work.

Profero Congratulates Jet Bank on the Launch of Albania's First 100% Digital Bank
Profero served as Jet Bank's preemptive incident response partner, deploying our Rapid-IR platform to secure Albania's first fully digital bank from day one.
We Said Wait. The Wait Is Over.
A year ago we said don't panic about quantum threats. That was correct. Here's what changed, and why the window for action is now.
We Added a Detection Rule. We Were Not Expecting This.
Claude Desktop runs its AI subprocess with --allow-dangerously-skip-permissions. What we found in the command line and what an attacker could do inside it.
The AI Incident Response Framework: When Your Agent Is the Threat
AI agents now cause incidents that look like ransomware, exfiltration, and insider threats. The framework Profero uses to tell the difference and respond.

The War Between Wars: How an IRGC Cyber Front Runs Destructive OT and IT Attacks Under Cover of a Ceasefire
An IRGC-directed persona sabotaged industrial refrigeration and wiped disks at Israeli sites during a ceasefire. How it unfolded and how to find the actor.
The AI produced malware kill switch
A Discord bot token hardcoded in every WindowsAudit binary let Profero monitor the attacker, pull their loot dump, and identify 25+ victim organizations.
WindowsAudit Backdoor: Inside a .NET RAT That Hides in Discord
Profero IRT reverse engineered WindowsAudit.exe, a .NET 8 RAT that uses Discord as C2, runs as SYSTEM, and tears down EDR in Safe Mode.
Everyone's Talking About Mythos. Here's What's Actually Going On.
What Anthropic's Claude Mythos release actually changes for defenders, based on the red team report, the community briefing, and the press coverage.
The Theater of Cyber War: How Russian "Hacktivists" Are Performing for Iran Without Actually Hacking Anything
Cardinal, Russian Legion, and RuskiNet are flooding Telegram with fabricated breach claims. We analyzed every major claim. All fake.
The Claude Code Leak: What One Missing File Cost Anthropic, and How to Check If You're Exposed
On March 31, 2026, Claude Code's full source shipped to npm via a missing .npmignore file. What was exposed and how to check if your packages leak too.
Why We Reforged Rapid-IR From the Ground Up
Rapid-IR: Reforged is the IR platform built by an incident response team. Proprietary AI, continuous readiness, and a 20-minute guaranteed response.
The Key Was on the Floor: How the FBI Director's Personal Accounts Were Already Exposed
How breach databases, stealer logs, and basic OSINT revealed the FBI Director's personal credentials, and what it means for executive security.
Hijacked at the Source: AppsFlyer's Trusted Marketing SDK Distributes a Crypto Stealer
Profero IRT has uncovered a cryptocurrency wallet hijacking supply chain attack in the AppsFlyer Web SDK
P4Tr!0T3CH Channel Doxxing & Disinfo Assessment
OSINT validation of a Hebrew-language Telegram channel claiming doxxing data and breach material on Iranian judiciary, IRGC, and APT35 targets.
địt mẹ mày morphisec: When Malware Authors Taunt Security Researchers
The complete analysis of Vietnamese Stealer - a Python-based info stealer using Telegram as a C2.
AtomicStealer Spreading via Fake Apple Support Websites
Profero uncovered an AtomicStealer campaign using a fake Apple Support site to trick macOS users into running a malicious bash command.
The $5 Million Letter: When Physical Mail Becomes Digital Extortion
Executives are receiving physical letters that impersonate ransomware groups like BianLian and demand $5 million in Bitcoin. How Profero spotted the scam.
New Attack Vector - AI - Induced Destruction
# From Friend to Foe: A New Era of Cybersecurity Incidents
From Drone Strike to File Recovery: Outsmarting a Nation State
How Profero helped recover ESXi data encrypted by DarkBit ransomware, a group suspected of nation-state ties, after the Isfahan drone attacks.
The Blurring Lines Between Financially Motivated Attacks and Nation-State Cyber Operations
Since 2022, Profero's IRT has investigated Russian threat actors in Europe, where profit-driven ransomware groups now operate with state-endorsed hacking.
Live Forensic Collection from Ivanti EPMM Appliances (CVE-2025-4427 & CVE-2025-4428)
Live forensic collection from Ivanti EPMM appliances hit by zero-days CVE-2025-4427 and CVE-2025-4428, from Profero's May 2025 incident response work.
Unmasking a Sophisticated Phishing Campaign: Profero IRT’s Deep Dive into a Global Microsoft Identity Attack
Profero IRT investigated a global phishing campaign on Microsoft 365 identities built on low-code platforms and phishing toolkits. Findings and defenses.
Understanding Quantum Cryptography: Separating Fact from Fiction
Quantum cryptography without the FUD: how quantum computers could break RSA and ECC, and what Quantum Key Distribution actually offers.
A Breach Is Inevitable: Why Organizations Are Failing in Proactive Threat Detection
Security teams buy CTEM, CSPM, and IDM tools, yet breaches still happen. Why tools alone fail at detection, with ransomware and data breach case studies.
Behind the Scenes: How Pager Apps Power 24/7 Incident Response Operations
**Behind the Scenes: How Pager Apps** **Power 24/7 Incident Response Operations**
MITRE ATT&CK: A Guidebook for the Cyber Jungle
A guide to MITRE ATT&CK, the non-profit knowledge base of attack groups, tactics, and tools founded in 2013, and how to read the threat landscape with it.
Secrets leakage – A rising threat. Development Practices to Safeguard Your Secrets
In 2024 Profero tracked attacks built on misconfigurations and leaked secrets in production. Best practices for managing credentials, API keys, and tokens.
Why Cyberattacks Spike During Holidays and How to be IR Ready
Every year, as we deck the halls and prepare to celebrate major holidays like July 4th,
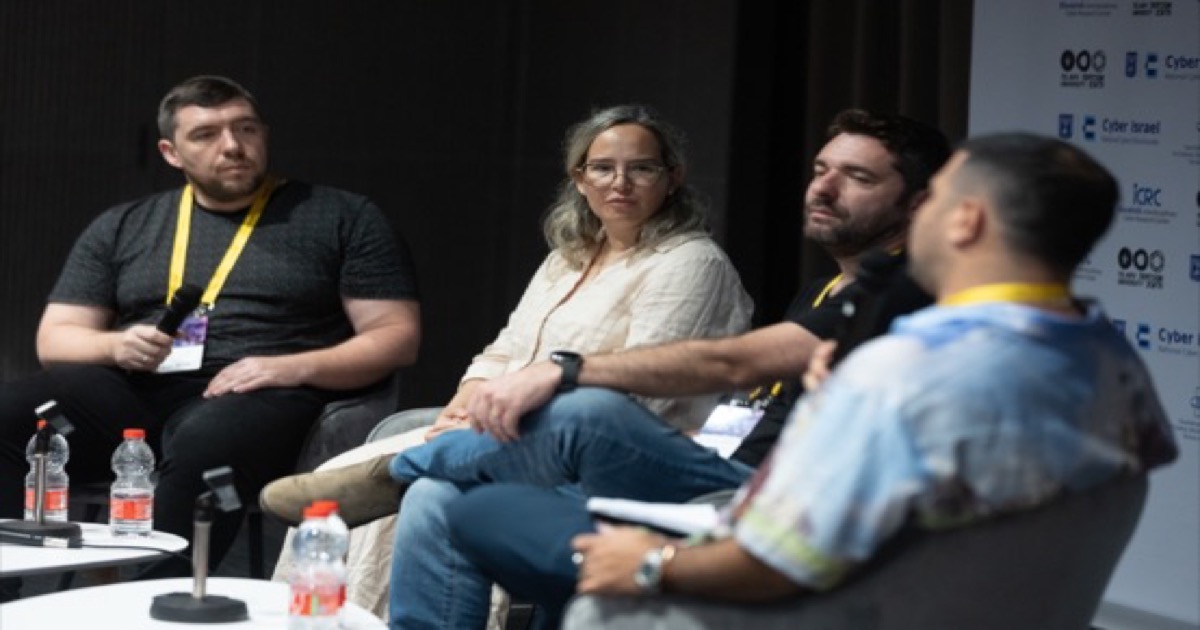
Cloud Security Alliance Conference: Attacker Perspective Panel Overview
Highlights from a Cloud Security Alliance Conference panel on cloud security from the attacker's perspective, featuring Profero CEO Omri Segev Moyal.
Microsoft Windows Endpoint Forensics Readiness Booster
Built-in Windows settings that improve forensics readiness for IT and security teams, with no extra tools. A short cheat sheet of key artifacts and logs.
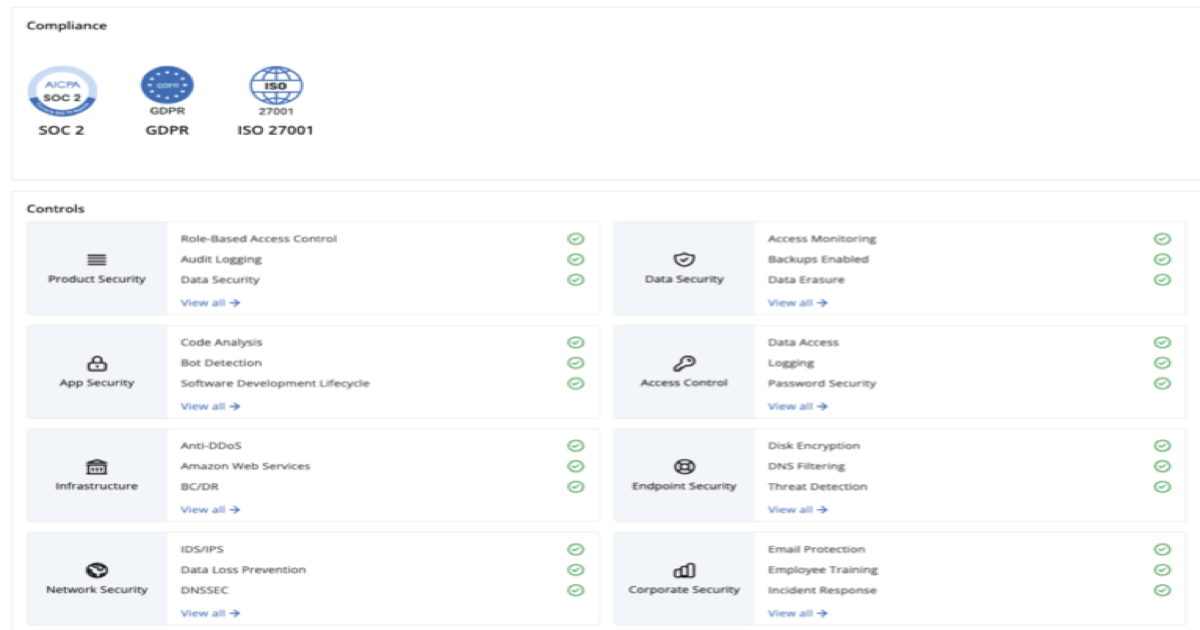
Profero is now Certified for SOC 2 (type 2) and ISO 27001
Profero is certified for SOC 2 Type 2 and ISO 27001 and launched a trust portal showing its security practices, controls, and certifications.
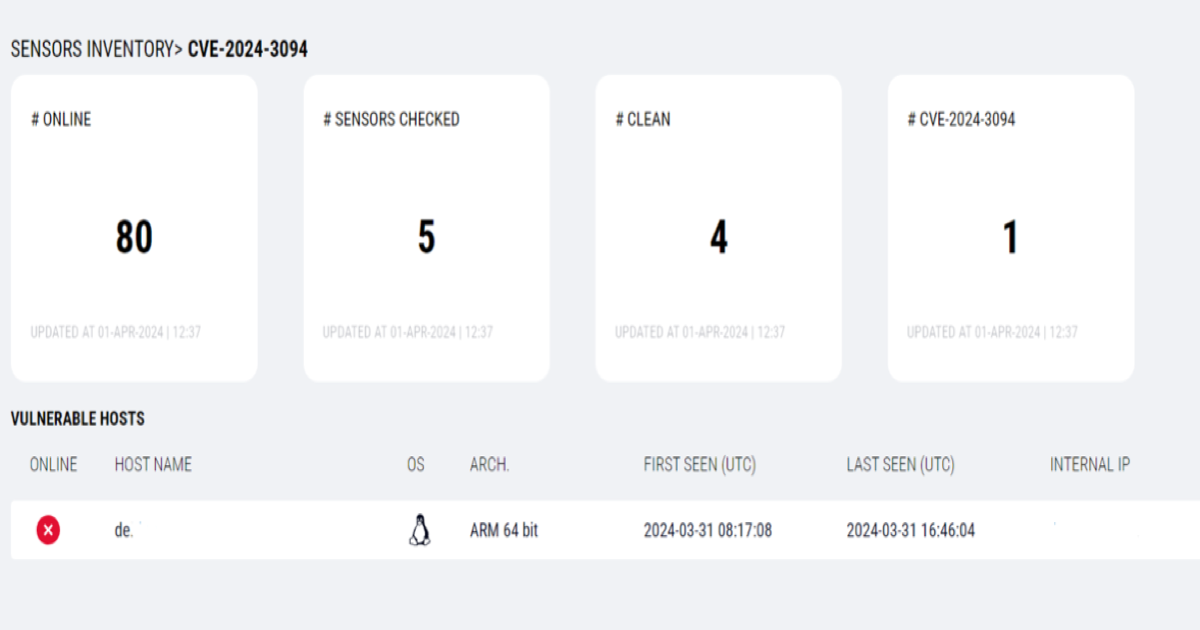
The 10.0 Rated CVE in xz-utils Jeopardizing SSH Security
CVE-2024-3094, rated 10.0: a backdoor planted by a maintainer in xz-utils, a Linux component, putting SSH security at risk. What it is and why it matters.
SysAid On-Prem Vulnerability Disclosure
SysAid disclosure of CVE-2023-47246, a zero-day in its on-premises software investigated with Profero. Customers should update to version 23.3.36.
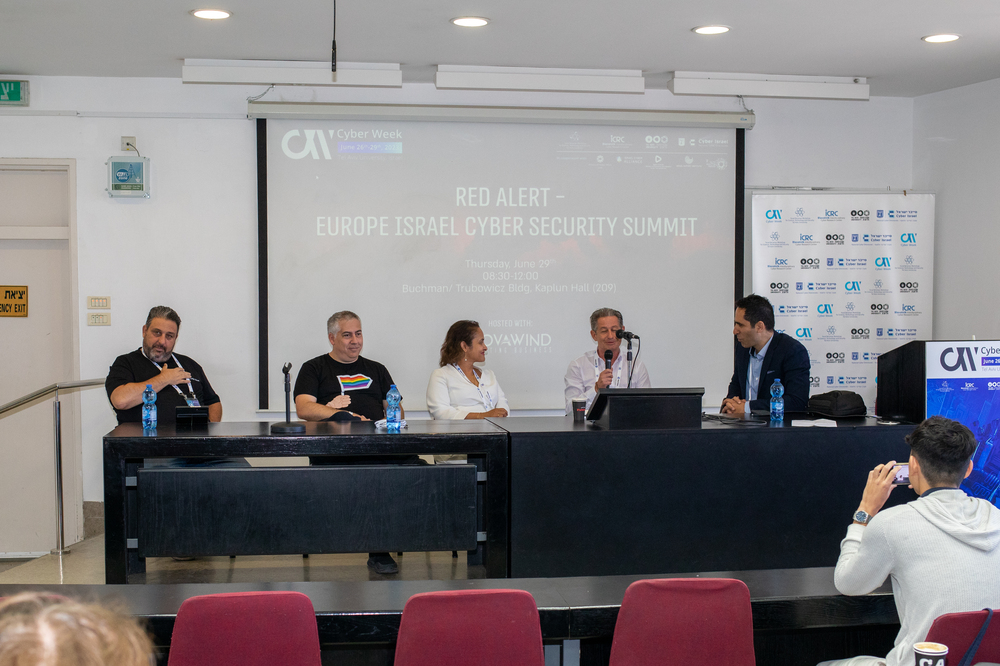
CyberWeek RedAlert 2023 Focus Shift: Parallels between Europe and Israel's Cyber Incident Response Preparedness
## Focus Shift: Parallels between Europe and Israel's Cyber Incident Response Preparedness
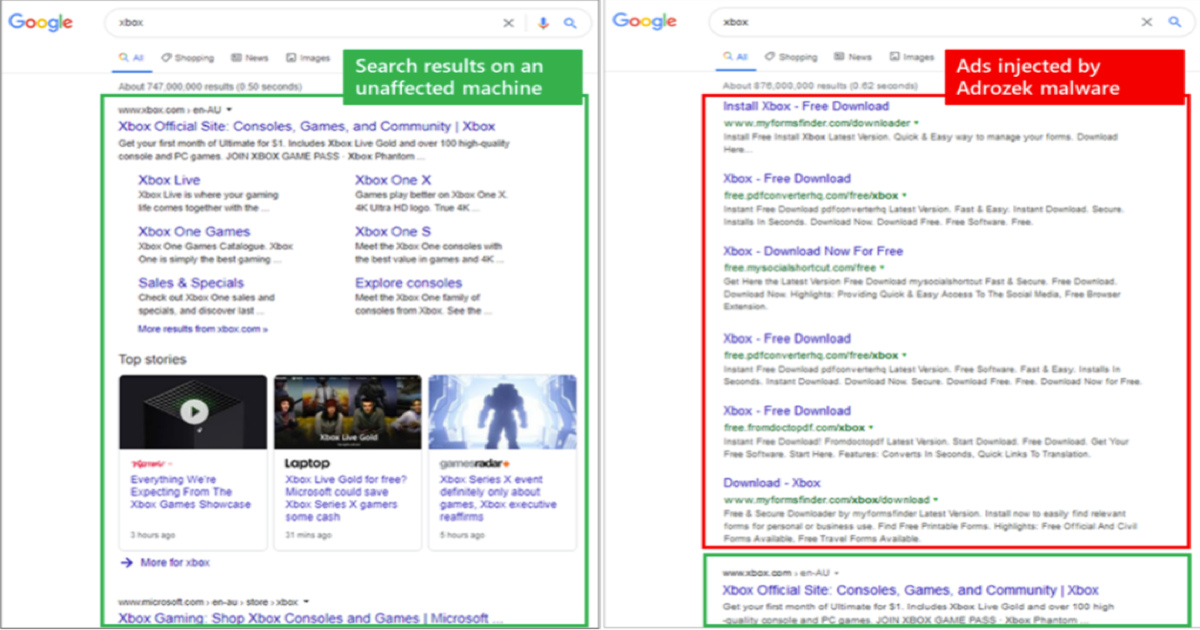
Malicious Extensions - What They Are And How To Fight Them
What malicious browser extensions are and how to fight them, starting from the 1.7 billion Chrome users who had extensions installed in 2020.
LastPass Breach - and your SSO
see our previous [**blog post**](https://profero.io/posts/lastpass_breach/)
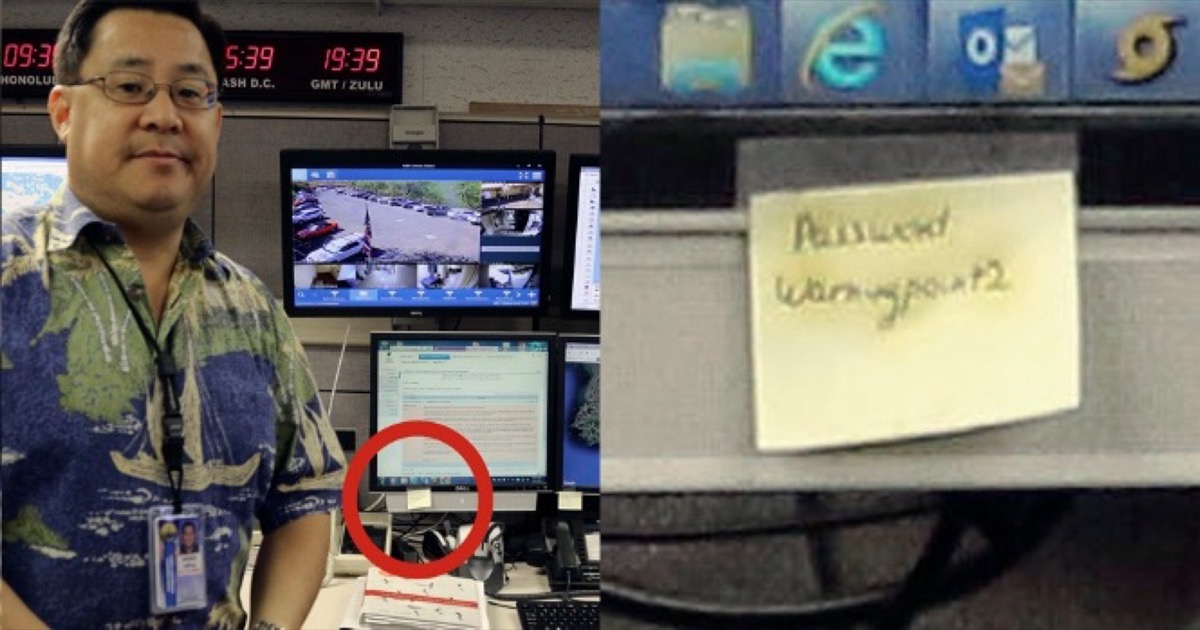
LastPass Breach - What went wrong?
**disclaimer: this is based on our experience, expertise, and public sources**
Online Programming Learning Sites Can Be Manipulated By Hackers To Launch Cyberattacks
Profero research on how attackers can hide their origin by launching cyberattacks from cloud IDEs on online programming learning sites.
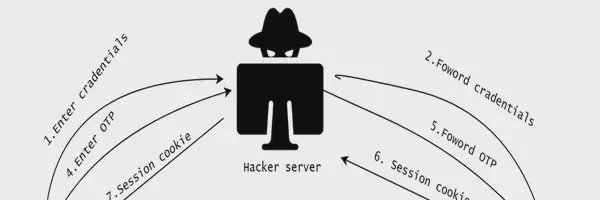
Multi-factor Authentication In-The-Wild bypass methods
How multi-factor authentication works, from SMS and authenticator apps to YubiKey, and the bypass methods attackers use against it in the wild.
Static unpacker and decoder for Hello Kitty Packer
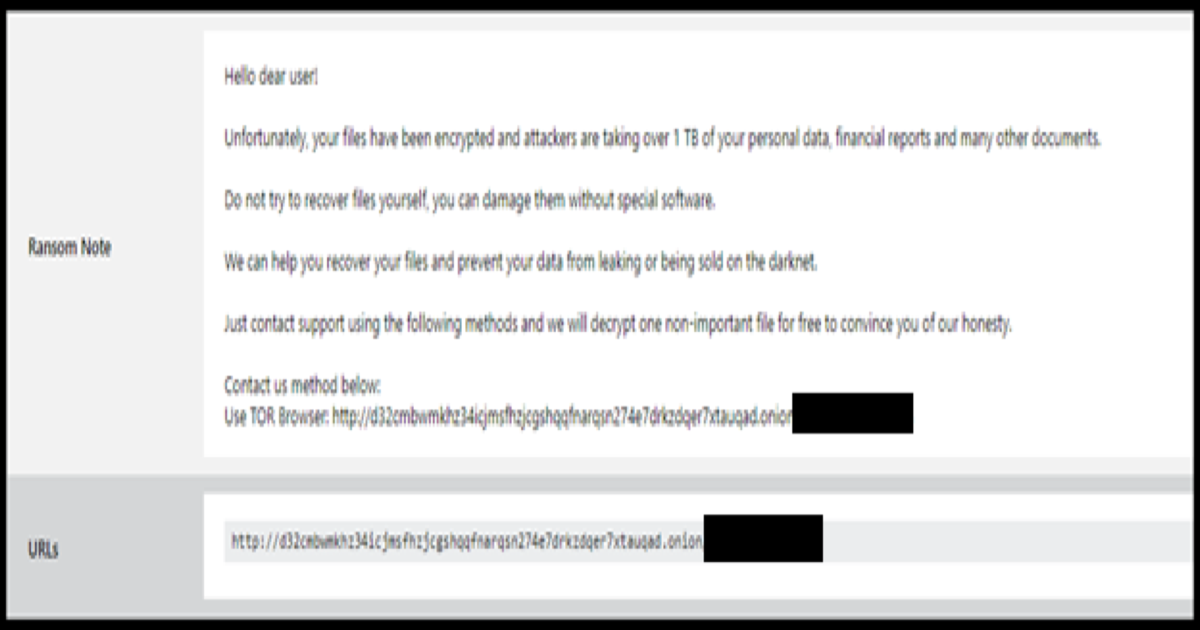
Profero releases a static unpacker and decoder for the Go packer that decrypts Hello Kitty ransomware's C++ payload in memory before running it.
OSS Getting Hammered for BigCorp Failures
Why the OSS model is broken, why log4j maintainers should not take the blame, and the $5,000 donation Profero pledged to the project.
log4jScanner
Profero built a scanner that finds log4j-vulnerable web servers on internal networks, so customers need not send server data to third parties.
Log4Shell & massive Kinsing deployment
On December 9th, 2021 news broke about a newly discovered vulnerability affecting the java logging library, Log4j.
From the Trenches: Common-Sense Measures to Prevent Cloud Incidents
Cloud breaches an IR team sees that could have been prevented, with case studies and advice on cloud provider APIs, training, and preparation.
RansomEXX, Fixing Corrupted Ransom
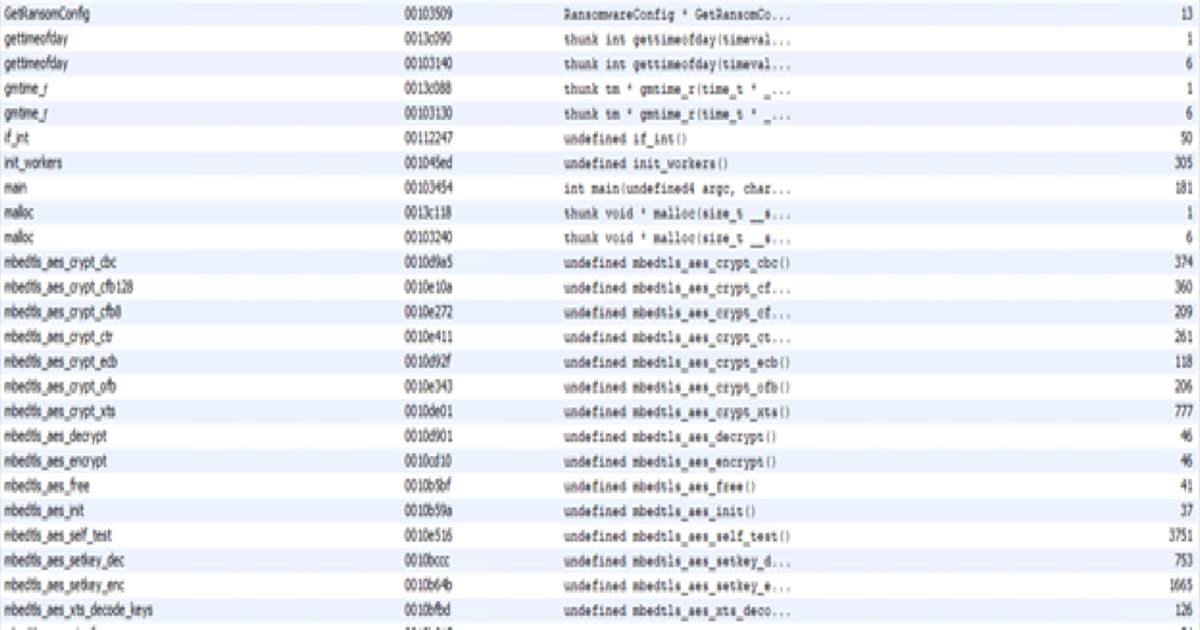
Profero found a bug in RansomEXX Linux ransomware that corrupts files, and released a tool that extracts keys from the attacker's decryptor to rescue them.
Secrets Behind Ever101 Ransomware
Profero IR analysis of Ever101 ransomware: a new file extension, a Music folder of dropped tools, and the toolset used to build an attribution profile.
Cuba Ransomware Group on a Roll
Profero and SecurityJoes investigated a Cuba ransomware attack that encrypted hundreds of machines using PowerShell, SystemBC, and Cobalt Strike.
APT27 Turns to Ransomware
How a Profero engagement during COVID-19 crossed the line between nation-state and cybercrime when APT27 turned to ransomware. Full report, no form.